
What changed
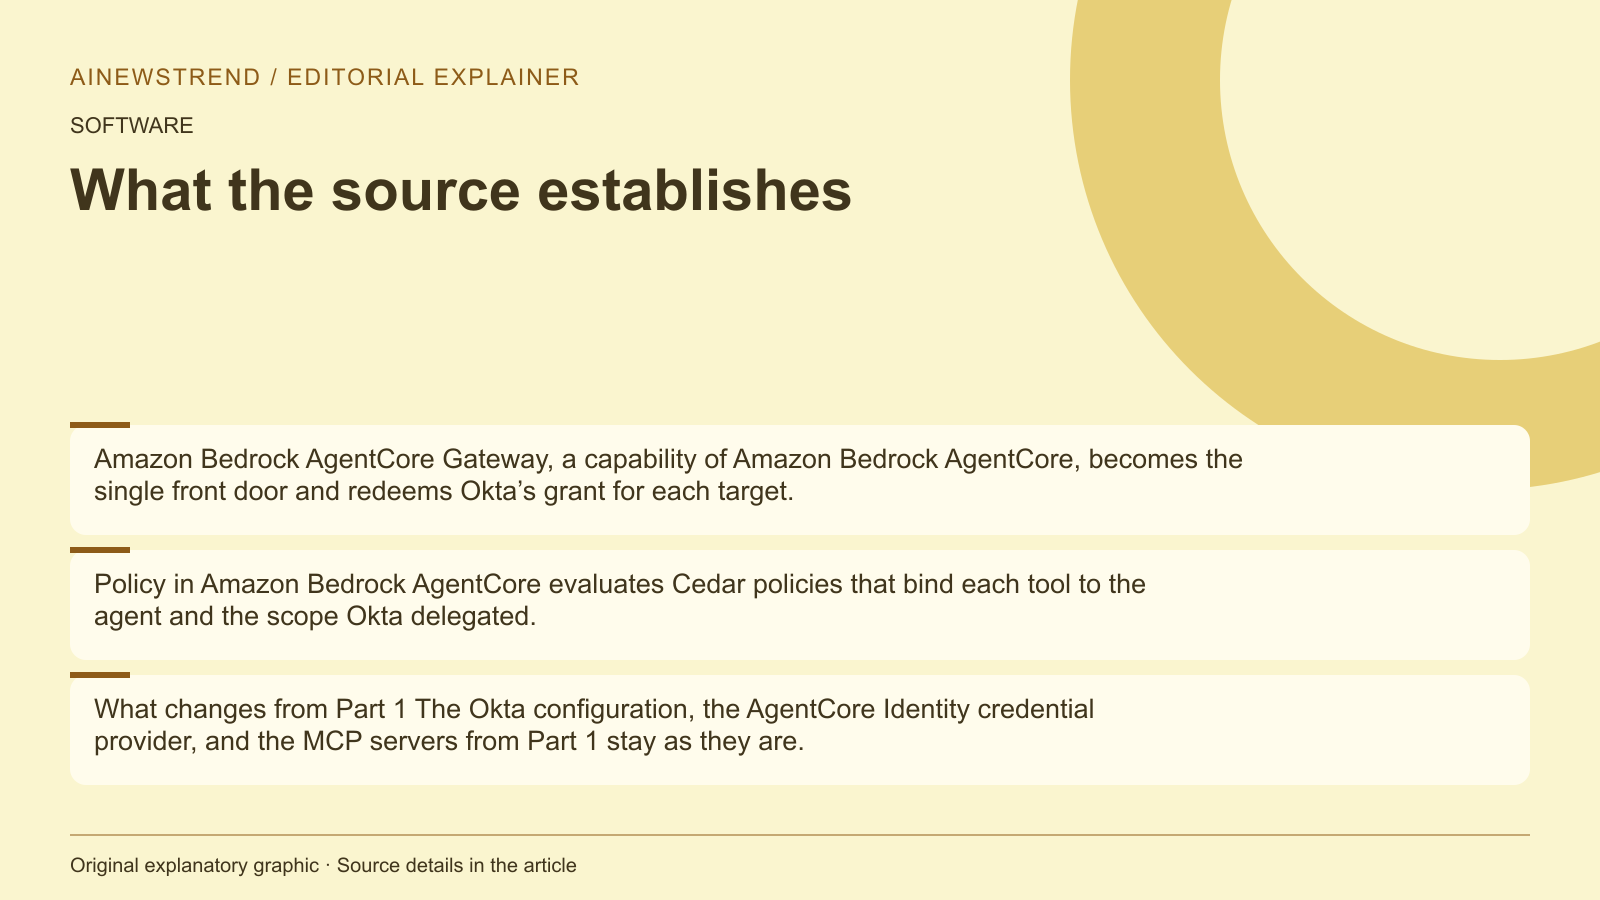
AWS has introduced enhancements to its AI agent access control framework by integrating Okta Cross App Access with Amazon Bedrock AgentCore. This update allows for more granular and scalable governance of AI agents, ensuring that only authorized users can interact with specific tools and resources. The new architecture introduces a centralized Gateway that handles authorization checks and token exchanges, streamlining the process for both agents and MCP servers.
What this means in practice
The updated system enables agents to securely access resources by leveraging Okta's grants through the AgentCore Gateway. This Gateway evaluates Cedar policies that bind each tool to the agent and the scope Okta has delegated. This setup ensures that each tool call is checked against predefined policies before execution, enhancing security and compliance. Additionally, the system supports multiple agents running on different platforms, such as Amazon Elastic Kubernetes Service (Amazon EKS), demonstrating the scalability of the new architecture.
Limitations and availability
The new features are part of the Amazon Bedrock AgentCore capabilities and require the use of Okta Cross App Access. The solution involves additional setup, including the configuration of the Gateway, policy engines, and observability tools like Amazon CloudWatch. The implementation may take around 90 minutes and involves costs related to Amazon EKS and AgentCore features. The provided code snippets are for non-production use and should be reviewed by security and legal teams before deployment. The supplied announcement does not specify exact performance benchmarks or detailed licensing conditions for the new features.